Securing identities.
Shaping what’s next.
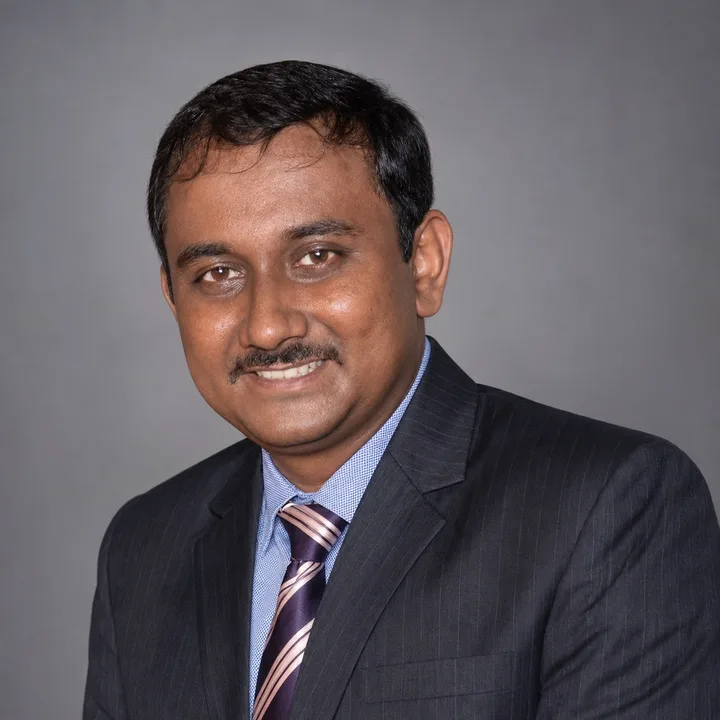
I'm Partho Sankar Roy, a cybersecurity director and Microsoft identity architect. For more than 15 years I've designed, secured and run enterprise identity: Active Directory and Entra ID, Zero Trust, privileged access, and now identity for AI agents.
Where strategy meets engineering.
Leadership grounded in hands-on technical depth, from directory internals to board-level risk conversations.
Identity & Access
- Microsoft Entra ID & Active Directory
- Hybrid identity & federation (ADFS)
- Passwordless & Windows Hello for Business
- Identity governance (IGA) & lifecycle
Security Architecture
- Zero Trust & Conditional Access design
- Privileged access (PAM) & Tier 0
- CIS benchmarks & posture assessment
- Certificate lifecycle & post-quantum readiness
AI & Non-human Identity
- Identity for AI agents
- Service principals & workload identity
- Credential hygiene & secrets
- Governance for agentic systems
Problems I've solved.
A few engagements from my consulting years. Clients are anonymised and details are kept general.
Passwordless at enterprise scale
Designed and deployed Windows Hello for Business with Cloud Kerberos Trust, which gave users phishing-resistant sign-in and seamless access to on-premises resources without a full PKI rollout.
A secure identity for a new company
Defined the Day-1 Entra ID security controls for a separated business, so the new entity could operate independently with a strong baseline from the first day.
Federation bridge between two organisations
Architected an interim ADFS federation bridge so users of a divested business kept access to shared applications during the transition services period, with a clear exit path.
Active Directory security assessment
Assessed a large AD estate against industry benchmarks and turned the findings into a prioritised remediation roadmap that leadership could act on.
Directory clean-up with leadership visibility
Led a stale-object clean-up across Active Directory, with a Power BI dashboard that gave leadership live progress and residual risk.
Non-human identity security
Developed a point of view and control-mapping framework for securing service accounts, workload identities and AI agents across major security frameworks.
Tools I build.
Personal projects that automate the identity security work I do every day. Select a tool to see what it does.
EntraShield
Scans a Microsoft 365 / Entra ID tenant against CIS Microsoft 365 benchmark controls and produces a prioritised, evidence-backed findings report.
- Read-only Microsoft Graph permissions
- Control-by-control pass / fail with evidence
- Remediation guidance ranked by risk
PS> Connect-MgGraph -Scopes 'Policy.Read.All','Directory.Read.All'
PS> Invoke-EntraShield -Benchmark CIS-M365

[+] Conditional Access policies ...... evaluated
[+] Authentication methods .......... evaluated
[!] Legacy authentication ........... finding
[+] Report exported: findings.html
Terminal output is illustrative. Tools are personal projects built and tested in lab tenants.
How ready are you to govern AI agents?
A 5-minute, 15-question self-assessment covering ownership, authentication, authorisation, monitoring and lifecycle. You get a maturity score and prioritised next steps, and your answers never leave your browser.
Notes from the field.
Practical thinking on identity, security and leadership.
Built through experience.
From running infrastructure to leading identity security for a global enterprise.
Infrastructure foundations
Windows Server, Active Directory and enterprise operations.
Directory & cloud identity
Hybrid identity, AD engineering and the move to Azure AD for global clients.
Specialist Leader, Identity & Cloud Security
Led Entra ID, Zero Trust, IGA, PAM, passwordless and AI identity engagements for UK and global clients.
Director, Cybersecurity
Leading workforce identity engineering and operations.
B.Sc. Electronics, University of Calcutta
Ideas begin with conversations.
Happy to talk identity security, speaking invitations, or swapping notes on securing AI agents.